Angora: Efficient Fuzzing by Principled Search
Peng Chen, Hao Chen

TL;DR
Angora is a novel mutation-based fuzzer that significantly improves software testing efficiency by increasing branch coverage through innovative constraint-solving techniques without relying on symbolic execution.
Contribution
It introduces scalable byte-level taint tracking, context-sensitive branch counting, gradient descent search, and input length exploration to enhance fuzzing performance.
Findings
Found almost all injected bugs in LAVA-M dataset
Detected more bugs than existing fuzzers in multiple programs
Achieved higher branch coverage and bug detection rates
Abstract
Fuzzing is a popular technique for finding software bugs. However, the performance of the state-of-the-art fuzzers leaves a lot to be desired. Fuzzers based on symbolic execution produce quality inputs but run slow, while fuzzers based on random mutation run fast but have difficulty producing quality inputs. We propose Angora, a new mutation-based fuzzer that outperforms the state-of-the-art fuzzers by a wide margin. The main goal of Angora is to increase branch coverage by solving path constraints without symbolic execution. To solve path constraints efficiently, we introduce several key techniques: scalable byte-level taint tracking, context-sensitive branch count, search based on gradient descent, and input length exploration. On the LAVA-M data set, Angora found almost all the injected bugs, found more bugs than any other fuzzer that we compared with, and found eight times as many…
Click any figure to enlarge with its caption.
 Figure 1
 Figure 2
 Figure 3
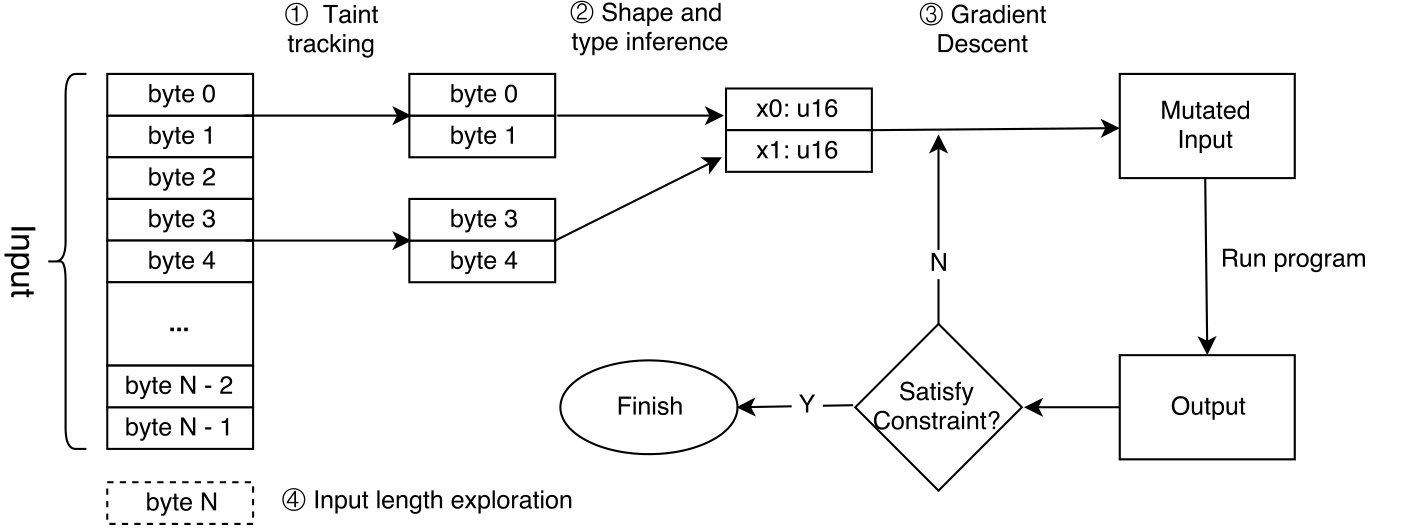 Figure 4
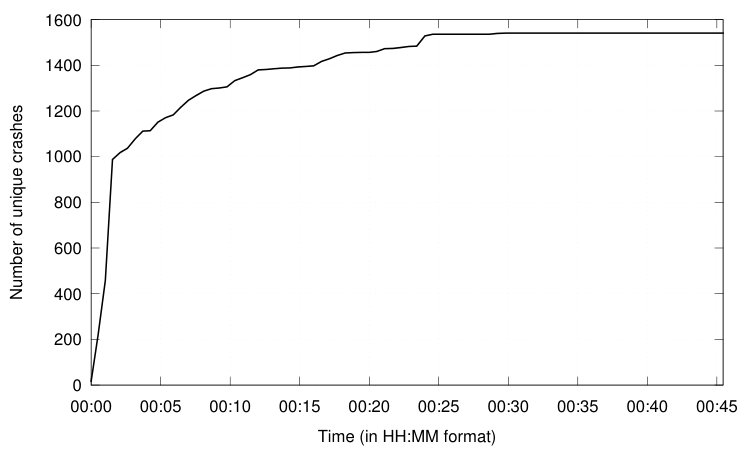 Figure 5
| Program | Listed | Bugs found by each fuzzer | |||||
| bugs | AFL | FUZZER | SES | VUzzer | Steelix | ||
| uniq | |||||||
| base64 | |||||||
| md5sum | Fail | ||||||
| who | |||||||
| Comparison | f | Constraint |
|---|---|---|
| Program | Listed | Found bugs | Time (min) | |
|---|---|---|---|---|
| bugs | Listed | Unlisted | ||
| uniq | ||||
| base64 | ||||
| md5sum | ||||
| who | ||||
| Program | Argument | Size | Line coverage | Branch coverage | Unique crashes | |||||
|---|---|---|---|---|---|---|---|---|---|---|
| (kB) | AFL | Increase | AFL | Increase | AFL | |||||
| file-5.32 | ||||||||||
| jhead-3.00 | ||||||||||
| xmlwf(expat)-2.2.5 | ||||||||||
| djpeg(ijg)-v9b | ||||||||||
| readpng(libpng)-1.6.34 | ||||||||||
| nm-2.29 | -C | |||||||||
| objdump-2.29 | -x | |||||||||
| size-2.29 | ||||||||||
| Metric | Non-context-sensitive | Context-sensitive |
|---|---|---|
| Line coverage | ||
| Branch coverage | ||
| Unique crashes |
| Program | Unique branches | Ratio | |
|---|---|---|---|
| Context insensitive | Context sensitive | ||
| file | |||
| jhead | |||
| xmlwf | |||
| djpeg | |||
| readpng | |||
| nm | |||
| objdump | |||
| size | |||
| Program | Random | Magic bytes | Gradient descent |
|---|---|---|---|
| + random | |||
| file | |||
| jhead | |||
| xmlwf | |||
| djpeg | |||
| readpng | |||
| nm | |||
| objdump | |||
| size |
| Program | Longer inputs | Average length | ||||
| Random | Random | missing | ||||
| Useful | Total | Useful | Total | |||
| file | 185 | 79k | 251 | 3342 | 889.9 | 399.0 |
| jhead | 0 | 66k | 0 | 26 | 0.0 | 0.0 |
| xmlwf | 277 | 143k | 588 | 2196 | 190.3 | 128.9 |
| djpeg | 32 | 106k | 474 | 3476 | 846.6 | 283.6 |
| readpng | 46 | 35k | 43 | 152 | 2242.7 | 363.1 |
| nm | 17 | 170k | 19 | 872 | 771.7 | 248.0 |
| objdump | 44 | 214k | 60 | 1614 | 1271.6 | 496.0 |
| size | 27 | 197k | 33 | 1482 | 1584.5 | 949.7 |
| Program | AFL | file | 971.17 | 791.73 |
|---|---|---|---|---|
| jhead | 2684.45 | 2648.91 | ||
| xmlwf | 2225.07 | 2206.24 | ||
| djpeg | 1439.94 | 1185.52 | ||
| readpng | 3374.43 | 2881.72 | ||
| nm | 1633.72 | 1045.35 | ||
| objdump | 1882.05 | 1192.04 | ||
| size | 1671.95 | 1174.55 |
Peer Reviews
No public reviews on file for this paper yet. If you reviewed it on a platform where reviews are public (OpenReview, ICLR, NeurIPS, ICML), you can paste yours below so the community can read it here.
Code & Models
Videos
No videos yet. Explain this paper in a talk, walkthrough, or lecture? Add one.
Taxonomy
TopicsSoftware Testing and Debugging Techniques · Software Engineering Research · Advanced Malware Detection Techniques
fficient Fuzzing by Principled Search
Peng Chen
ShanghaiTech University
Hao Chen
University of California, Davis
Abstract
Fuzzing is a popular technique for finding software bugs. However, the performance of the state-of-the-art fuzzers leaves a lot to be desired. Fuzzers based on symbolic execution produce quality inputs but run slow, while fuzzers based on random mutation run fast but have difficulty producing quality inputs. We propose new mutation-based fuzzer that outperforms the state-of-the-art fuzzers by a wide margin. The main goal of to increase branch coverage by solving path constraints without symbolic execution. To solve path constraints efficiently, we introduce several key techniques: scalable byte-level taint tracking, context-sensitive branch count, search based on gradient descent, and input length exploration. On the LAVA-M data set, und almost all the injected bugs, found more bugs than any other fuzzer that we compared with, and found eight times as many bugs as the second-best fuzzer in the program who. so found 103 bugs that the LAVA authors injected but could not trigger. We also tested eight popular, mature open source programs. und 6, 52, 29, 40 and 48 new bugs in file, jhead, nm, objdump and size, respectively. We measured the coverage of d evaluated how its key techniques contribute to its impressive performance.
1 Introduction
Fuzzing is a popular technique for finding software bugs. Coverage-based fuzzers face the key challenge of how to create inputs to explore program states. Some fuzzers use symbolic execution to solve path constraints [5, 8], but symbolic execution is slow and cannot solve many types of constraints efficiently [6]. To avoid these problems, AFL uses no symbolic execution or any heavy weight program analysis [1]. It instruments the program to observe which inputs explore new program branches, and keeps these inputs as seeds for further mutation. AFL incurs low overhead on program execution, but most of the inputs that it creates are ineffective (i.e., they fail to explore new program states) because it blindly mutates the input without taking advantage of the data flow in the program. Several fuzzers added heuristics to AFL to solve simple predicates, such as “magic bytes” [25, 19], but they cannot solve other path constraints.
We designed and implemented a fuzzer, called , that explores the states of a program by solving path constraints without using symbolic execution. acks the unexplored branches and tries to solve the path constraints on these branches. We introduced the following techniques to solve path constraints efficiently.
The reference list from the paper itself. Each links out to its DOI / PubMed record.
- 1[1] “American fuzzy lop” URL: http://lcamtuf.coredump.cx/afl/
- 2[2] Sofia Bekrar, Chaouki Bekrar, Roland Groz and Laurent Mounier “A taint based approach for smart fuzzing” In IEEE International Conference on Software Testing, Verification and Validation (ICST) , 2012, pp. 818–825
- 3[3] “Binary fuzzing strategies: what works, what doesn’t” URL: https://lcamtuf.blogspot.sg/2014/08/binary-fuzzing-strategies-what-works.html
- 4[4] Marcel Böhme, Van-Thuan Pham and Abhik Roychoudhury “Coverage-based greybox fuzzing as markov chain” In Proceedings of the 2016 ACM SIGSAC Conference on Computer and Communications Security , 2016, pp. 1032–1043
- 5[5] Cristian Cadar, Daniel Dunbar and Dawson R Engler “KLEE: unassisted and automatic generation of high-Coverage tests for complex systems programs.” In OSDI 8 , 2008, pp. 209–224
- 6[6] Cristian Cadar and Koushik Sen “Symbolic execution for software testing: three decades later” In Communications of the ACM 56.2 , 2013, pp. 82–90
- 7[7] Sang Kil Cha, Maverick Woo and David Brumley “Program-adaptive mutational fuzzing” In Security and Privacy (SP), 2015 IEEE Symposium on , 2015, pp. 725–741
- 8[8] Sang Kil Cha, Thanassis Avgerinos, Alexandre Rebert and David Brumley “Unleashing mayhem on binary code” In Security and Privacy (SP), 2012 IEEE Symposium on , 2012, pp. 380–394